Four Technical Articles
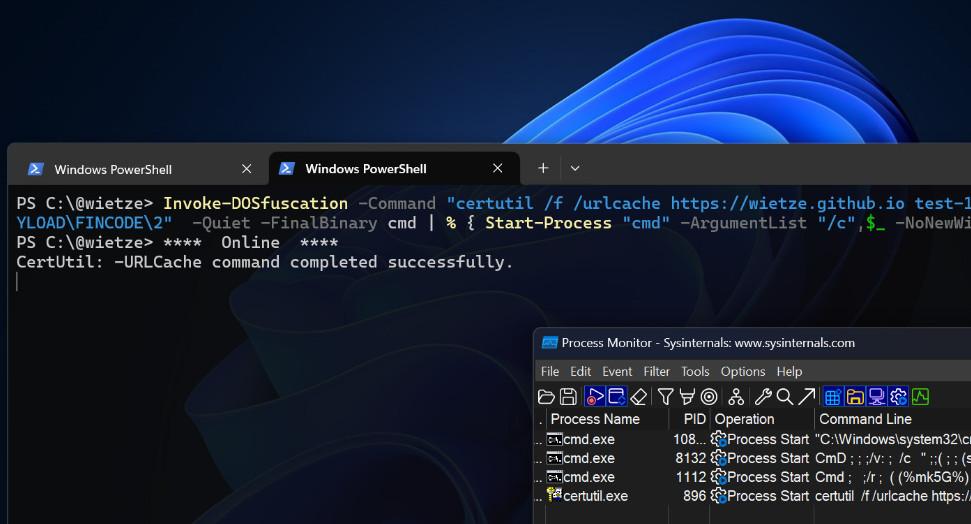
Bypassing Detections with Command-Line Obfuscation
Defensive tools like AVs and EDRs rely on command-line arguments for detecting malicious activity. This post demonstrates how command-line obfuscation, a shell-independent technique that exploits executables’ parsing “flaws”, can bypass such detections. It also introduces ArgFuscator, a new tool that documents obfuscation opportunities and generates obfuscated command lines.
Certified Red Team Operator (CRTO) - Notes
Name : CRTO - Red Teaming Command Cheat Sheet (Cobalt Strike)
How to Bypass WAF in 2025: Challenges and Solutions
How many times has a site blocked the requests made by your web scraper? Most of the time, that's due to WAFs, application-level firewalls that come with several defense systems to block undesired traffic.
They rely on several advanced techniques, but keep calm! There's always a way to get around them. Here, you'll learn how to bypass WAF protections and scrape any site.
Let's learn how!
Paged Out! is a free experimental (one article == one page) technical magazine about programming (especially programming tricks!), hacking, security hacking, retro computers, modern computers, electronics, demoscene, and other similar topics.
It's made by the community for the community. And it's not-for-profit (though in time, we hope it will be self-sustained) - this means that the issues will always be free to download, share, and print.